Penetration testing for MSPs, without handing over the keys.
One person clicks a link and the test begins. Galactic follows the routes an attacker would take through identity, network and endpoints, and an analyst reviews every finding before it reaches you.
The method is protected by U.S. Patent No. 12,373,572.
How a test runs
From the first click to a reviewed report, with nothing installed along the way.
-
Send a link
Straight to the user whose machine and environment are being analyzed.
-
The user clicks
The assessment launches and runs while they carry on working.
-
Galactic goes to work
Identity layer, network and endpoints, following the routes an attacker would take to reach what matters.
-
You get the report
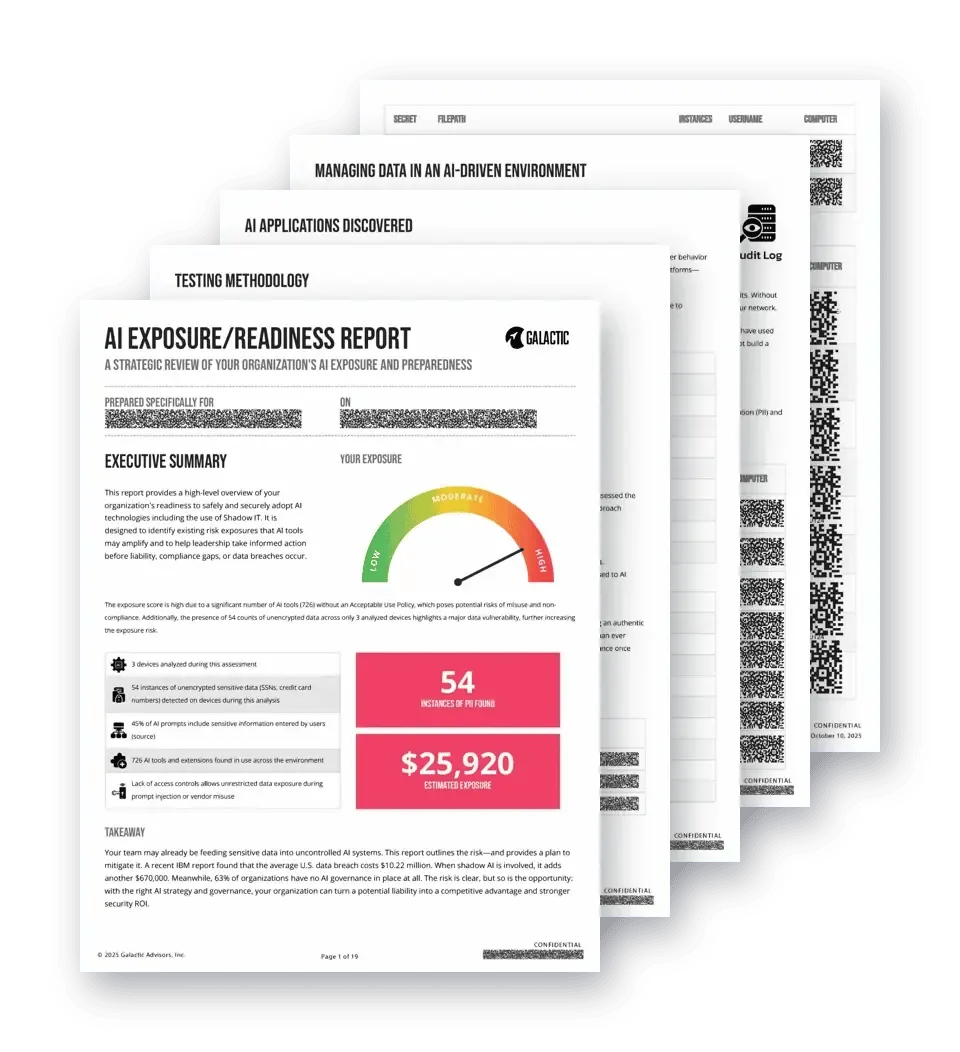
Our team reviews every finding first and sorts it by severity, so the first thing you read is the first thing worth fixing.
Each test measures against the last, so you can show progress over time.
What it checks
The places attackers get in today. Everything we find is yours, and exports into the tools your team already uses.
Microsoft 365
Configuration and account settings that leave the identity layer open.
Firewall
What your rules are really letting through.
Active Directory
Where account and permission setups create a path to more access.
Credentials
Weak, reused and browser-stored passwords.
Dark web
Your logins turning up in known breaches.
Tested by people who didn't build your stack
When the same team grades its own work, that's a conflict of interest, not a security program.
Your test is run by an independent, third-party team, not the people who built your stack or manage it day to day. We have nothing to gain from what we find, which is what makes the report worth trusting in the first place.
- 25,000+
- assessments run. Every environment we test sharpens how we find what matters first.
- Every report
- reviewed by our own analysts before it reaches you.
- Patented
- user-activated testing that never asks for administrative credentials.
Your environment first, then every client's
Clients, insurers and auditors increasingly ask you to show that the security you manage is working. Test your own house, then extend the same test to everyone you protect.
-
GalacticWatch
Your own MSP
Quarterly penetration testing of your environment, monthly vulnerability analysis, a risk report every stakeholder can follow, and unlimited prospecting scans. Your security posture, tested to the same standard you extend to clients.
-
CyberWatch
Every client you protect
Recurring penetration testing across every enrolled client, with client-ready reporting you present under your own engagement. Simple to deploy, simple to sell, and priced so every environment can be tested, even those that never have been.
-
Baseline analysis
Any environment, even one you don't manage
A snapshot of a prospect's security posture with no credentials and no agent install, and a report that gets the security conversation started. Included with GalacticWatch.
For executivesWhat the findings mean for the organization, in plain terms, so you can act on what matters most.
For IT and security teamsThe attack paths in full detail, so you know exactly what to fix and where.
More than 1,000 MSPs share what works, what breaks and how they price it.
Weekly Power Hour sessions, monthly SecOps training live and on demand, and 1:1 onboarding and guidance from our Account Management team. Peers and analysts in your corner, not a ticket queue.
Next up: the Security Stack Workshop on December 9th. Free, virtual and open to all.
The people behind every assessment
 Anna TalericoChief Executive Officer
 Seth LoePresident and Chief Security Officer
 Cody KretsingerDirector of Security Research
See what a test finds on a real environment
Book a demo and we'll walk you through what Galactic finds on a real environment, yours or a client's.
Rather talk now?
Already a partner? Log in to the portal.
Thanks. On the live site this request would go to the Galactic team.